A $20k bank transfer lands in your queue. The account looks fine, the device looks fine, and the probability of fraud is low.
You still want to look at it, right?
It’s because of how we intuitively calculate risk:
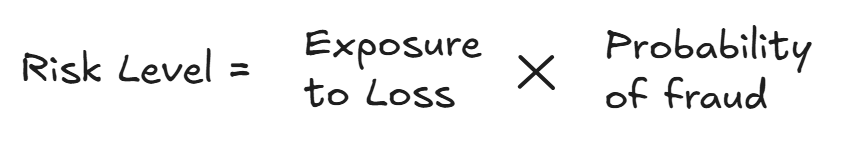
That $20k? That’s the exposure talking.
Fraud fighters obsess over risk, so you weigh every decision by how much you could lose and how likely you are to lose it.
When the amount is big enough, it skews your judgment regardless of the probability of fraud.
A while back I wrote about the overlooked truth about false positives. How data vendors are judged by how they can help you detect fraud rather than what they’re truly good at - detecting false positives.
The same can be said about how fraud teams look at their leads. While reducing FPs is a primary task of all teams, they mainly obsess over fraud signals.
But here’s the thing:
You’re already doing the hard part when identifying fraud signals. You’ve pulled the data, found the signal, and analyzed it.
But if you put in 5% more effort, you can get a second signal that solves a different problem - false positives.
It’s just a matter of perspective, nothing more.
The mirror image of fraud
Here’s how you do it.
Just take the same exposure and probability lens you already use, and run it backwards.
Let me give a deliberately stripped-down heuristic that shows the principle (do NOT try it at home).
That $20k transfer is high exposure, which is exactly why it felt like a fraud signal. Now flip it and look at a $2 bank transfer instead.
Even if other signals of the transfer would make its probability of fraud high, would you still call it high risk?
Probably not. Being wrong costs you two dollars, being right costs you much more in processing.
Of course, that’s a simplification.
In practice you’re not approving every $2 transaction or blocking every $20k one, and amount alone tells you very little about intent.
So here’s a more nuanced example.
Effort and intent
Say you’re trying to stop fraudulent sellers on a marketplace.
You open a new shop for review, and it looks like someone generated it in a hurry.
There are only a handful of listings, the descriptions are short and generic, the pictures look AI-generated, and the whole thing reeks of carelessness.
You know this shop. You’ve seen it a hundred times.
And even if you didn’t, would a legitimate seller treat their own shop like that?
So you read it the way every fraud team does. Low effort suggests fraud intent. Fraud intent means a high probability of fraud, and a high probability of fraud means high risk.
But if lack of effort shows fraud intent - what does high effort show?
Does a high-effort store show intent to be a legitimate seller? And if so, what does a high-effort store look like?
The answer is simple - exactly the opposite of the one you just reviewed.
Dozens of listings, added over weeks and months instead of all at once. Descriptions with details only someone holding the product would know. Pictures that aren’t rehashed, reskinned, and repeated over and over, because someone actually took them.
All of that came straight from your fraud description, turned inside out.
Now, let me be clear - flipping a fraud signal doesn’t prove someone isn’t a fraudster. Just as a fraud signal on its own doesn’t prove fraud.
You still want to validate it over historical data, combine it with other signals, and weigh the ROI of using it.
Because that’s what you do when you develop a new solution. But now you have a new source for FP leads - your very own fraud signals.
Every rule, twice
Theories aside, how do you use it in practice outside a brainstorming session?
You make it a habit.
Every time an analyst writes a fraud rule, they stop and ask one extra question - can I flip this signal and use it to identify legitimate events?
When the answer is yes, there are a few ways to use it.
The simplest one is an exclusion inside the fraud rule itself. Here’s an illustrative version:
IF listing_count < 5 AND description_length < 50 AND duplicate_images = TRUE
AND NOT (shop_age_days > 90 AND original_images_ratio > 0.8)
THEN send to review
Or you write a separate approval rule that runs on top of your fraud rules and lets the high-effort sellers through.
Or you auto-resolve those items straight out of the manual review queue, so your analysts never have to review high-effort shops.
Each option cuts false positives using a heuristic you already identified, only in reverse. The data work is the same and the rule logic barely changes - you just asked one extra question.
And for most fraud teams I talk to, false positives are the more pressing problem anyway, at least most of the year.
The bottom line
You already describe fraud in detail, in every rule and every vendor evaluation. Describe your good users just as carefully - it costs you about 5% more effort.
Just take any signal you’ve identified or developed for fraud detection, and flip it. Does it help you describe legitimate behavior or intent?
How are you developing signals to identify false positives? Hit reply and tell me how - I read every one.
In the meantime, that’s all for this week.
See you next Saturday.
P.S. If you feel like you're running out of time and need some expert advice with getting your fraud strategy on track, here's how I can help you:
Free Discovery Call - Unsure where to start or have a specific need? Schedule a 15-min call with me to assess if and how I can be of value.
Schedule a Discovery Call Now »
Consultation Call - Need expert advice on fraud? Meet with me for a 1-hour consultation call to gain the clarity you need. Guaranteed.
Book a Consultation Call Now »
Fraud Strategy Action Plan - Is your Fintech struggling with balancing fraud prevention and growth? Are you thinking about adding new fraud vendors or even offering your own fraud product? Sign up for this 2-week program to get your tailored, high-ROI fraud strategy action plan so that you know exactly what to do next.
Sign-up Now »
Enjoyed this and want to read more? Sign up to my newsletter to get fresh, practical insights weekly!